Cloud Infrastructure Hardening: Zero-Trust Defense Protocols for High-Growth Tech Companies
A tactical cybersecurity guide on cloud infrastructure hardening, zero-trust perimeter defense, API vulnerability mitigation, and penetration testing workflows.
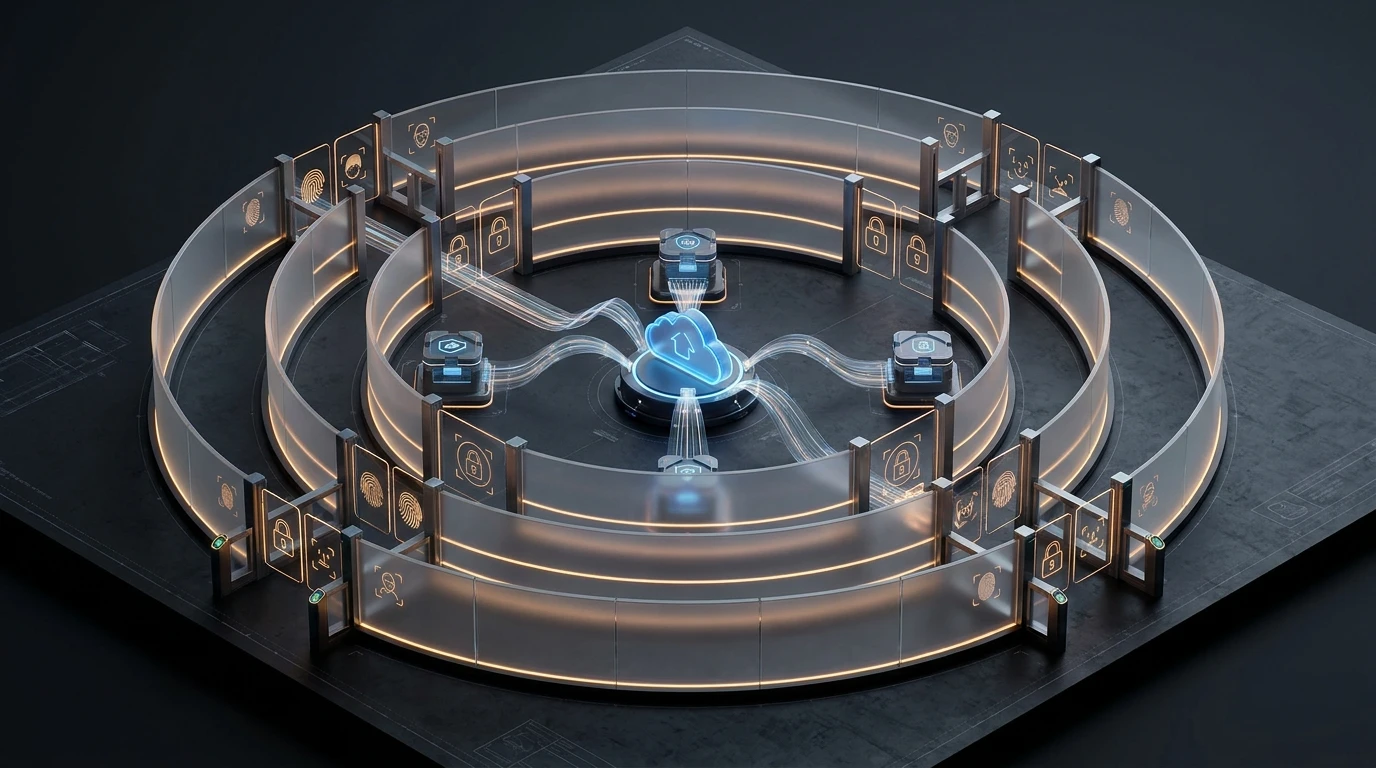
Futuristic 3D cryptographic glass shield with violet and amber cyber defense perimeter rings — Documented by CyberSolu Research & Development.
Core Insights from CyberSolu
- 1Over 80% of modern cloud breaches originate from misconfigured Identity and Access Management (IAM) roles and exposed API keys rather than zero-day exploits.
- 2Enforcing strict Zero-Trust Architecture (ZTA) requires mutual TLS (mTLS), ephemeral credentials, and least-privilege role boundaries.
- 3Continuous automated DevSecOps vulnerability scanning in CI/CD pipelines intercepts security flaws before deployment.
- 4Regular penetration testing workflows validate perimeter resilience against credential stuffing, SSRF, and privilege escalation attacks.
- 5Security by CyberSolu provides comprehensive digital asset defense and infrastructure hardening for growing brands.
The Shifting Landscape of Cyber Threats #
In modern cloud computing, the traditional concept of a "castle-and-moat" corporate network is dead. With distributed engineering teams, multi-cloud microservices, third-party SaaS integrations, and serverless architectures, there is no single physical perimeter left to defend.
Recent threat intelligence demonstrates that over 80% of cloud security breaches do not exploit sophisticated zero-day code vulnerabilities. Instead, they exploit mundane oversights:
- Wildcard IAM permissions (
Resource: "*", Action: "*"). - Exposed development environment API tokens in public Git histories.
- Unauthenticated internal microservice communication endpoints.
- Unpatched container dependencies with critical Remote Code Execution (RCE) flaws.
For fast-moving tech companies and digital brands, security cannot be an afterthought bolted on right before an acquisition or compliance audit. It must be built directly into the foundation.
The 4 Pillars of Cloud Hardening #
Hardening your cloud footprint requires applying defense-in-depth across every layer of the infrastructure:
1. Identity & Access Management (IAM) Sanitization #
The most critical attack vector in AWS, Google Cloud, and Azure is privilege escalation through over-permissioned service accounts.
- Eliminate Permanent Keys: Prohibit long-lived secret access keys. Enforce short-lived STS tokens (maximum 60-minute TTL).
- Least-Privilege Role Boundaries: Restrict microservice roles strictly to the specific database table, S3 bucket, or Redis instance they require.
- Hardware-Bound MFA: Require FIDO2/WebAuthn hardware security keys for all engineering access to production environments.
2. Zero-Trust Network Architecture (ZTA) #
Never assume that traffic inside your Virtual Private Cloud (VPC) is safe. If a single microservice is compromised via Server-Side Request Forgery (SSRF), an attacker can pivot across the entire internal network.
- Enforce mutual TLS (mTLS) for all service-to-service communication.
- Isolate production database clusters inside private subnets with no public IPv4 addresses.
- Mandate bastion jump hosts with ephemeral SSH keys for administrative access.
The DevSecOps Pipeline: Catching Vulnerabilities in CI/CD #
Security testing should never wait for an annual manual penetration test. By integrating automated vulnerability scanners directly into GitHub Actions or GitLab CI, security bugs are caught before pull requests are merged.
| Stage | Security Tooling | Verification Objective |
|---|---|---|
| Commit | Secret Scanners (Gitleaks, Trufflehog) | Prevent accidental API key leaks |
| Build | Static Application Security Testing (SAST) | Detect insecure code patterns & injection risks |
| Containerization | Container Vulnerability Scanners (Trivy) | Flag unpatched base image CVEs |
| Deployment | Dynamic API Fuzzers & DAST | Verify authentication headers and endpoint boundaries |
Defensive Engineering with CyberSolu #
At CyberSolu, we recognize that digital growth and security are two sides of the same coin. An e-commerce brand scaling to eight figures or a SaaS company processing sensitive customer transactions cannot afford downtime, reputational damage, or data leakage.
Through our upcoming division Security by CyberSolu (security.cybersolu.com), we are developing enterprise-grade cloud defense systems, automated vulnerability auditing frameworks, and penetration testing protocols tailored for high-velocity ventures.
Key Answers & Clarifications
Daniyal Rashid
CyberSolu LeadFounder & Growth Engineer
Daniyal heads strategy and technical architecture at CyberSolu, guiding performance marketing systems, custom Next.js engineering, and cybersecurity hardening across venture projects.
Connect on LinkedInTurn these frameworks into measurable enterprise value.
We don’t do generic retainers. CyberSolu builds specialist-led growth ventures across performance marketing, custom software architecture, and cybersecurity defense.